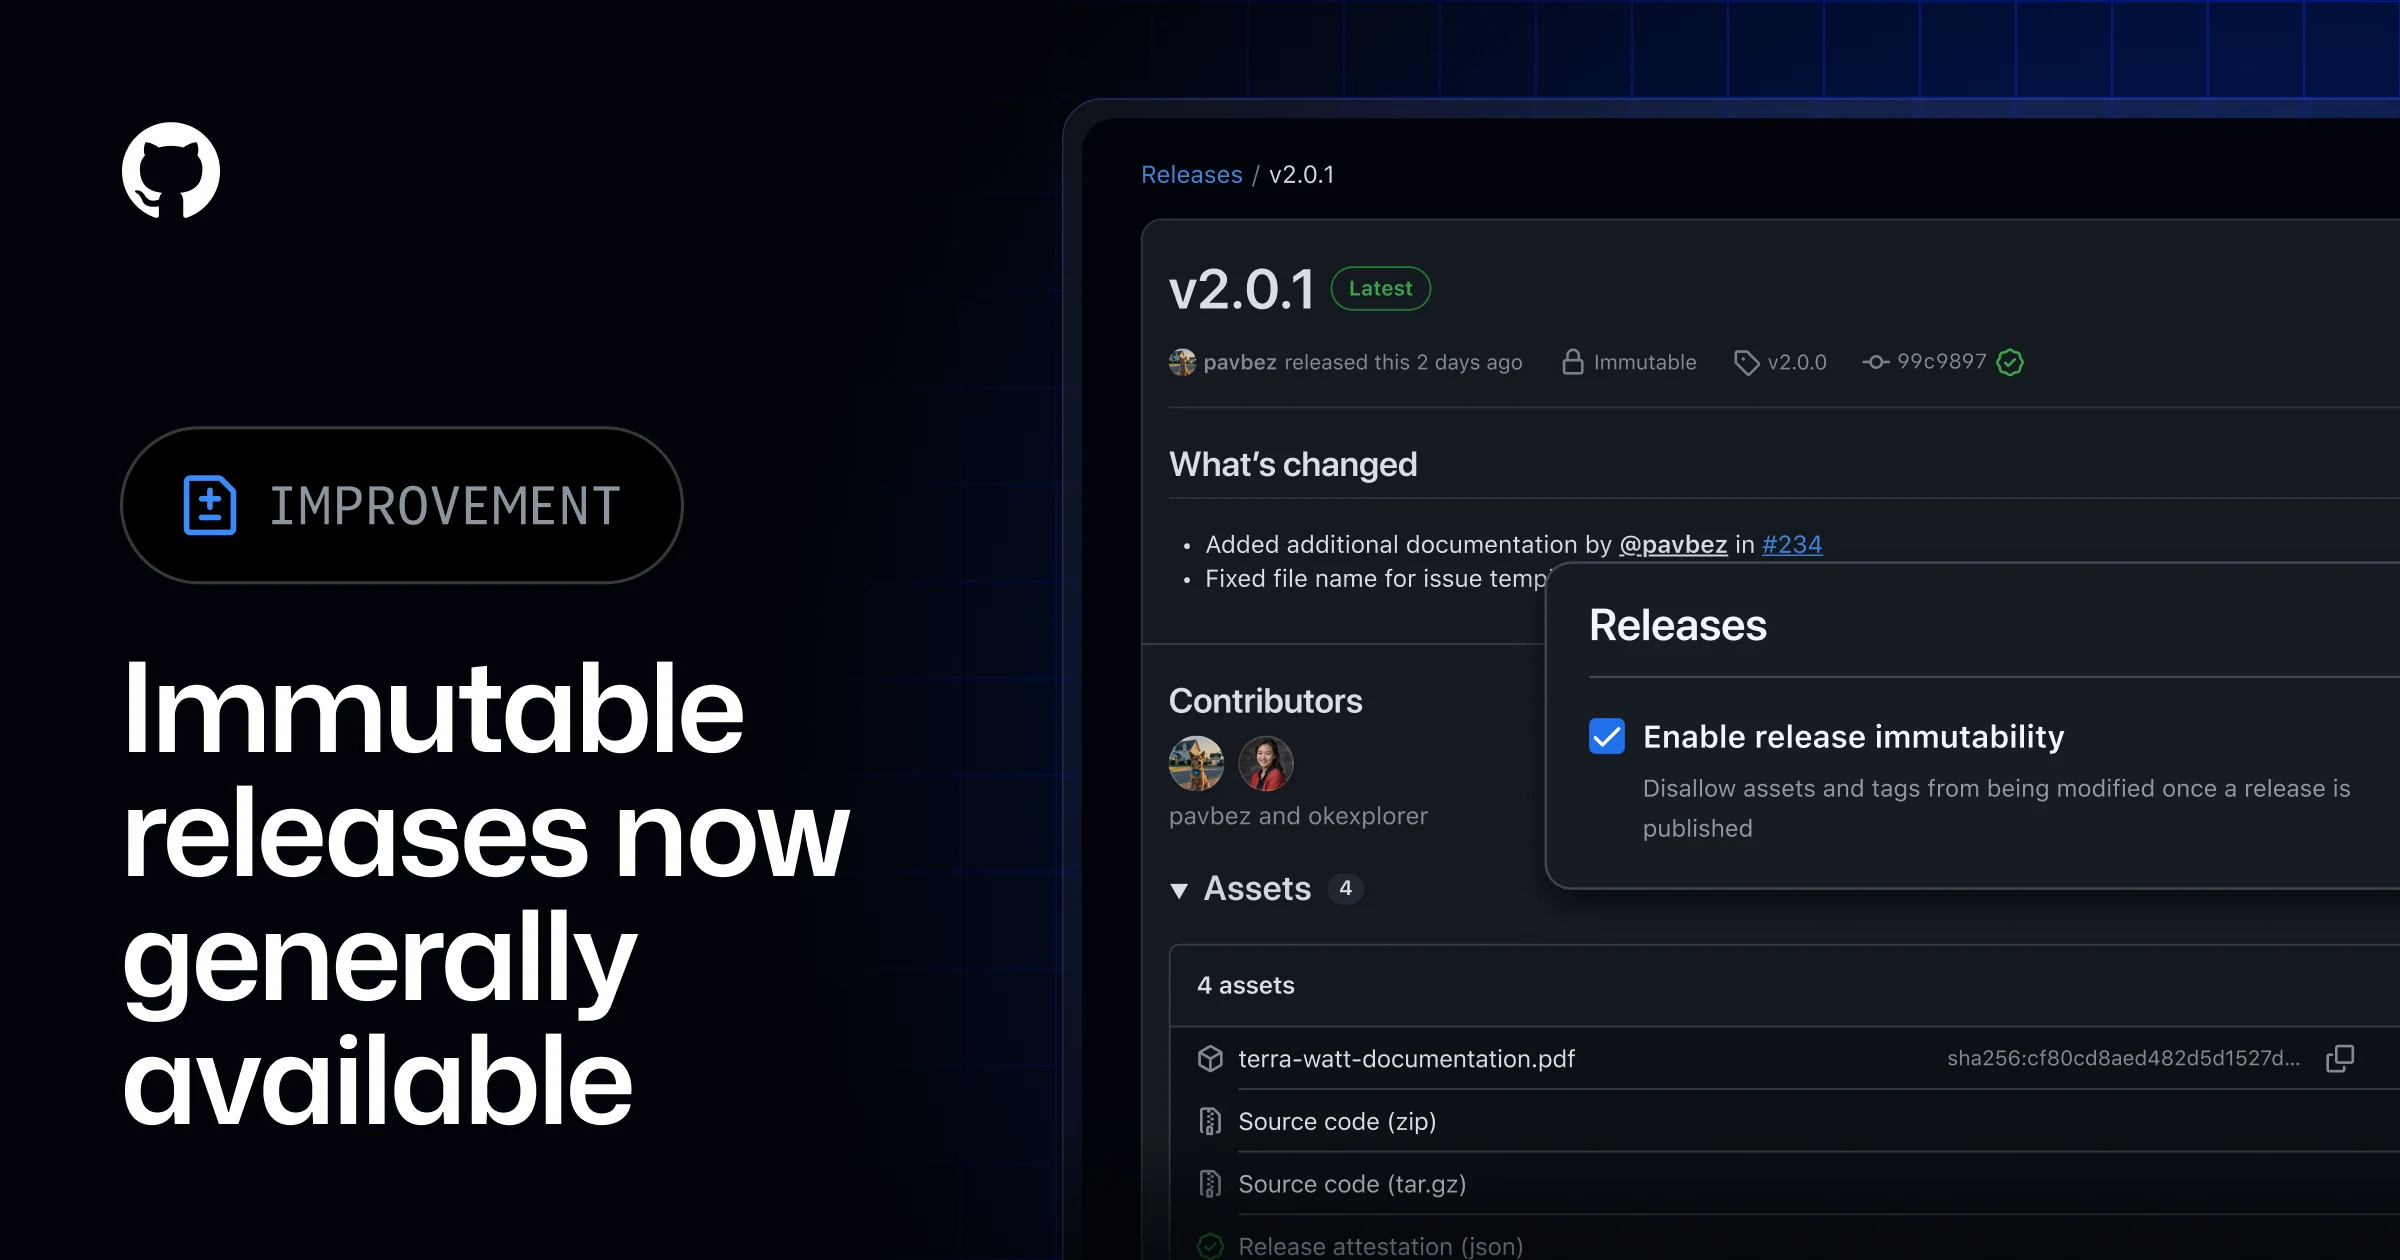
What was announced
GitHub announced general availability of immutable releases. The feature protects published release assets and tags and provides release attestations to support verification of their integrity. Read the official announcement.
Ackrolix implementation perspective
A dependable release process needs to answer which artifact was approved and which artifact reached the environment. If a published binary or tag can change without an obvious trail, an incident review becomes harder. Artifact integrity complements tests and approvals; it does not make untested software safe.
Ackrolix would review how a delivery pipeline builds, identifies and promotes artifacts. The same approved build should move through review and production stages rather than being rebuilt with unknown differences. Recovery procedures also need an identifiable prior version, with database compatibility checked before a rollback is attempted.
For a scoped implementation, explore Ackrolix’s quality assurance and testing in Gurgaon.
What this means for a team in Gurgaon
Gurgaon product teams formalising release approvals. For a Gurgaon engagement, map the existing customer or employee journey before defining the implementation scope. Identify the records that currently move between teams, the person responsible for each approval and any integration access still needed. A working review environment should let those users validate the change before the wider rollout.
Questions to take into your project review
- Identify the artifact approved for each release.
- Verify provenance during promotion.
- Test rollback with compatible database changes.
Turn the announcement into a clear delivery decision
Share your current application, the workflow you want to improve and the systems it needs to connect. Ackrolix can review the change, identify dependencies and define a phased implementation with acceptance checks.